beemNet
beemNet is a secure corporate network, the core of beem, available in four Security Editions. It provides the foundation for secure connectivity and protection by integrating users, devices, applications, and sites into a private network architecture.
Connected devices and networks are protected from internet-based cyber threats, and privacy is enhanced through targeted anonymisation and encryption. beemNet enables secure internet browsing and application access, supports modern cryptographic authentication methods such as passkeys, and prevents connected devices from being directly exposed to the internet.
Designed for scalability, high availability, and seamless integration with existing network and security infrastructures, beemNet reduces operational and management overhead.
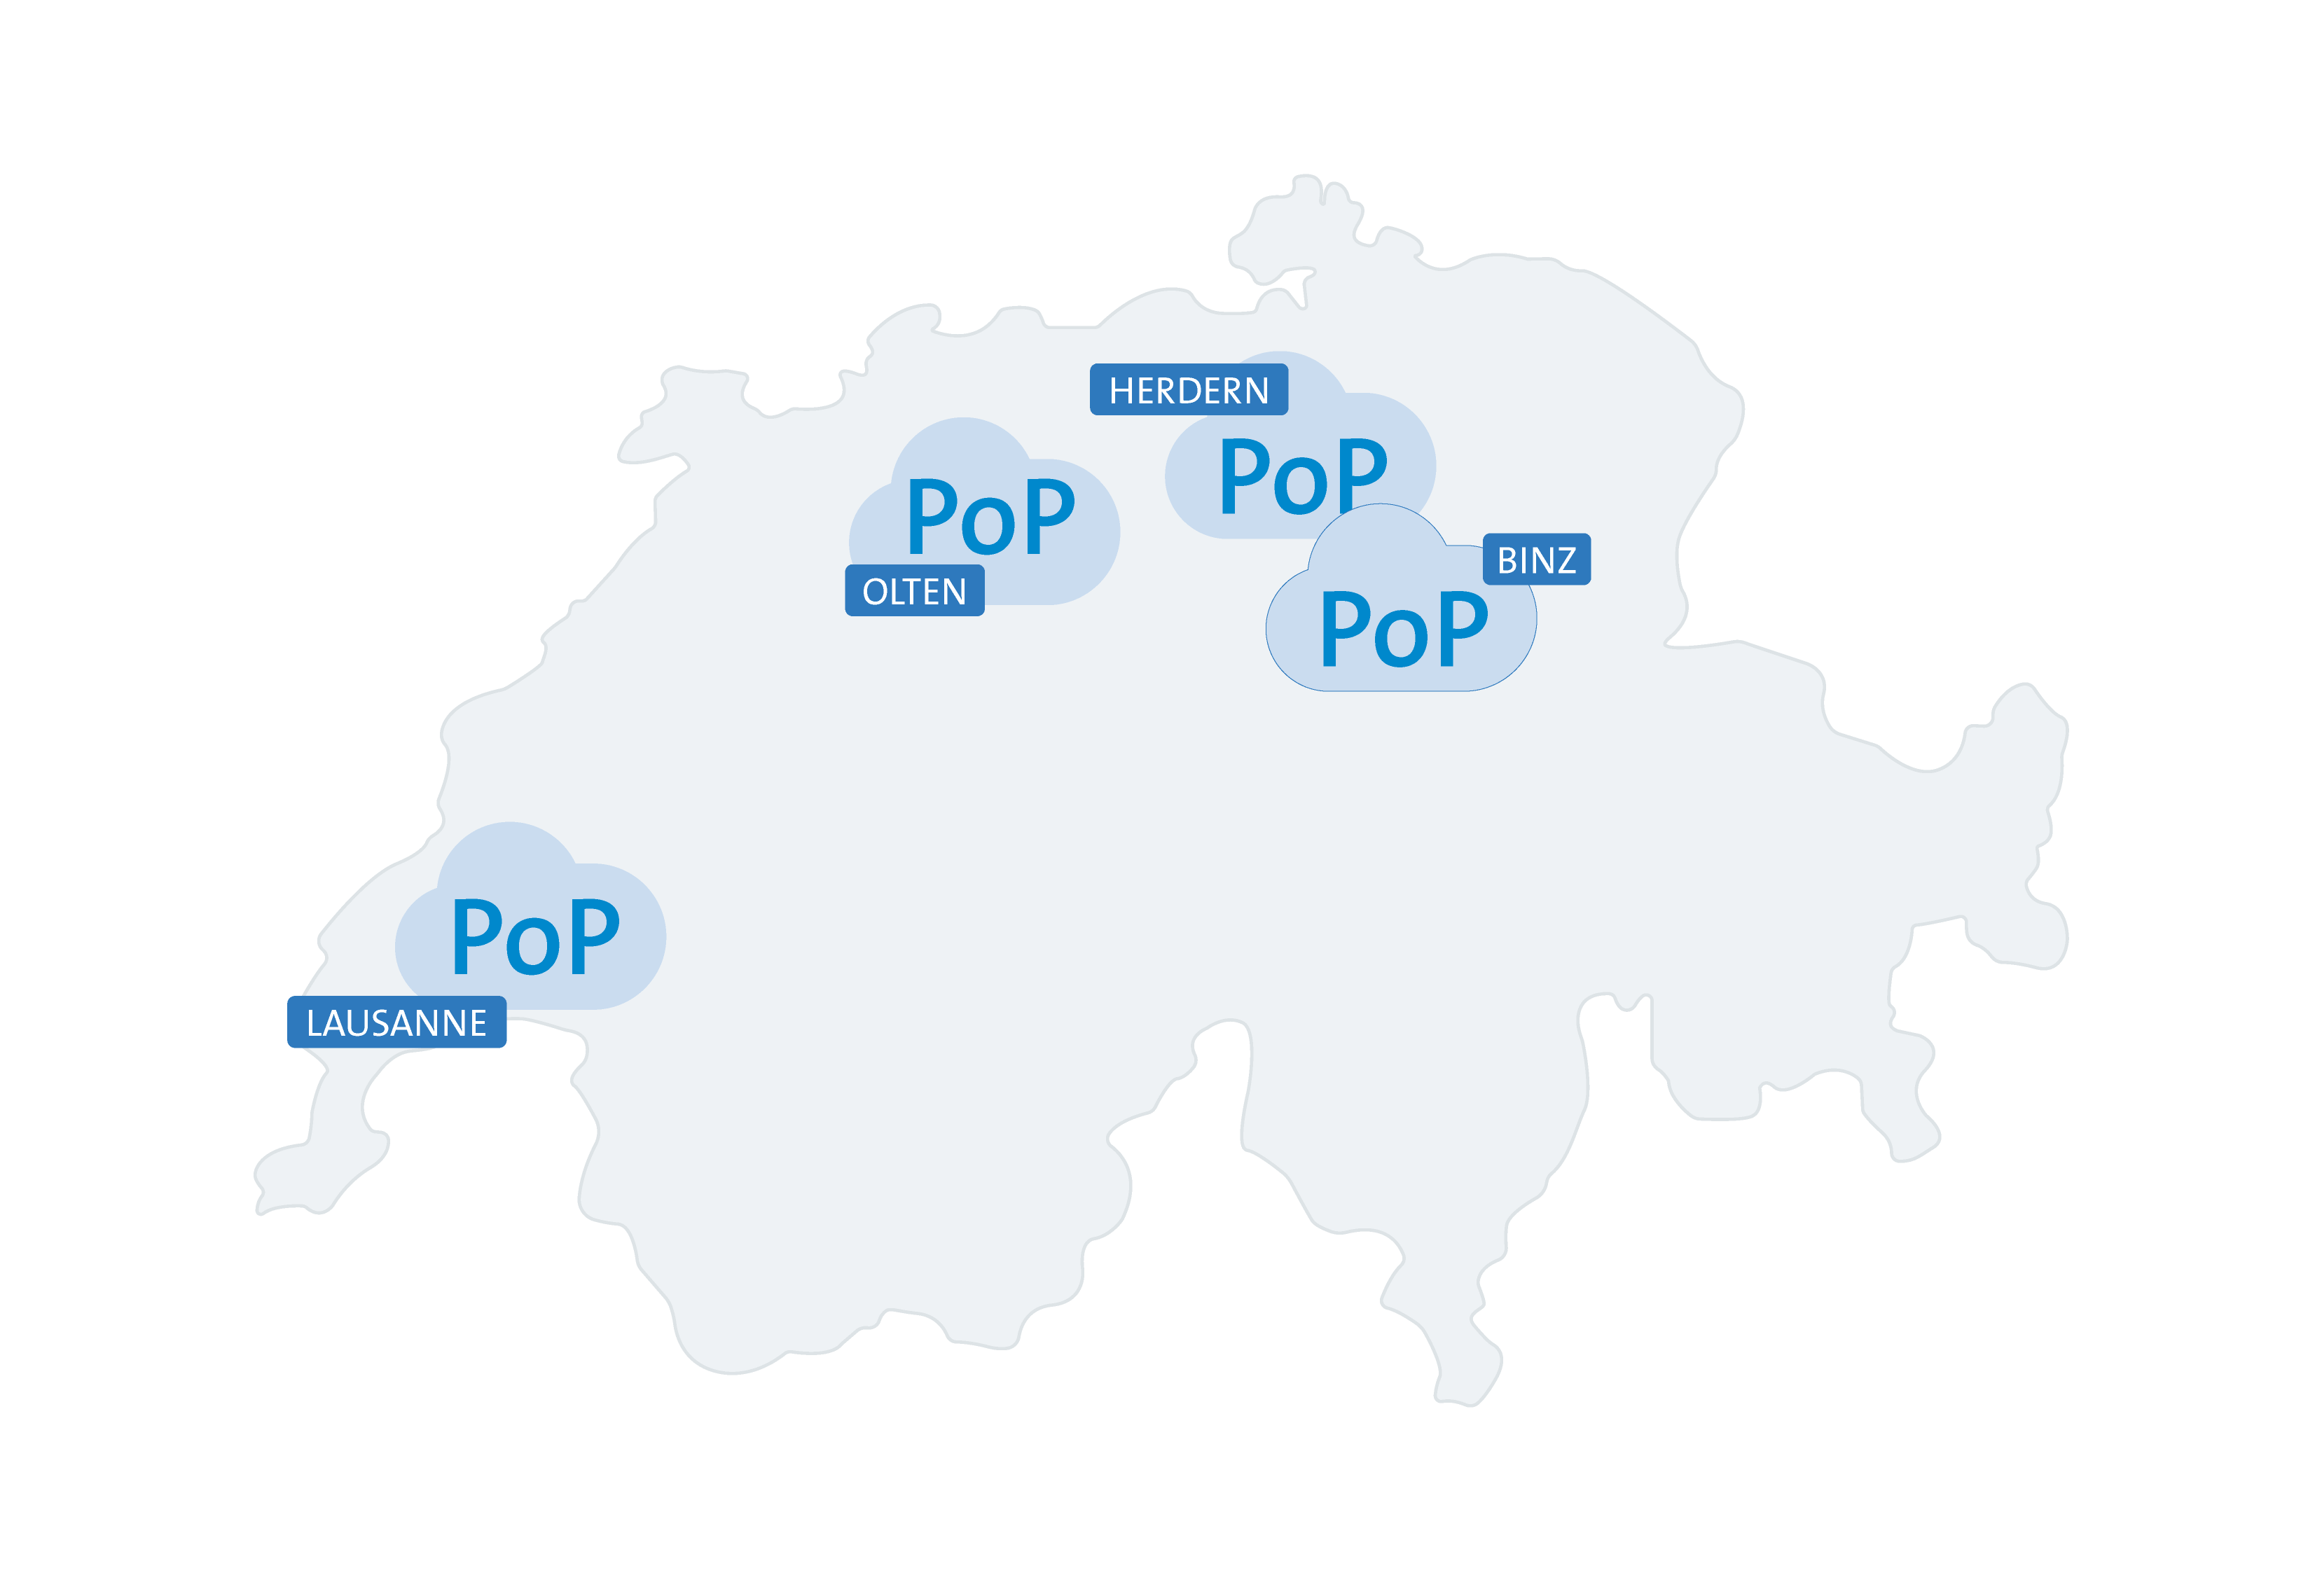 Swisscom operates four geographically redundant beem Points of Presence (PoP) in Switzerland. Built-in automatic failover mechanisms redirect traffic to another PoP if one becomes unavailable.
Access to beemNet
Access to beemNet is provided through site and user licences:
- Site licences combine beemNet options with a site connection, integrating the site into beemNet.
- User licences for mobile subscriptions are beemNet options linked to user identities. They grant authenticated users access to the associated functionalities.
Users who do not have a mobile connection, or whose mobile connection cannot be combined with the service, can be integrated through a separately offered user licence without a mobile subscription (Protect License).
Devices can connect to beemNet in two ways:
Agentless: Connecting a device to beemNet without the beem app. The connection is established either through a beem SIM on the Swisscom mobile network or through a beem-protected Swisscom internet connection. Agentless connections do not provide protected connectivity on external networks such as public Wi-Fi or foreign mobile networks while roaming.
Agent-based: Connecting a device to beemNet using the beem app. The app establishes a secure VPN connection to beemNet that provides end-to-end protected access across networks, including public Wi-Fi and international roaming. Agent-based connections also support advanced security features such as malware detection, device posture management, Deep Packet Inspection (DPI), and granular access control.
For more information, see the device onboarding page.
Secure roaming with the beem app
Devices using an agentless mobile connection (SIM-based) are securely connected to beemNet while operating on the Swisscom mobile network. However, this protection does not apply when the device is roaming abroad.
Because of technical limitations in roaming and foreign mobile network (RAN) architectures, beem cannot provide an end-to-end secure connection to beemNet for agentless devices connected through foreign mobile networks.
To maintain end-to-end protected access to beemNet while abroad, devices must use an agent-based connection via the beem app, which must be installed and active.
Zero Trust Network Access
Zero Trust Network Access (ZTNA) enables secure access to individual enterprise applications. Every access request is evaluated based on user identity, device, and context. Access to the approved application is granted only if the defined conditions are met.
Unlike traditional VPN or remote access solutions, ZTNA does not provide users with general access to a corporate network. Instead, only the specific application that is required is made accessible—for example, a CRM system, accounting software, an intranet, or an internal web application.
The security status of the user, device, and access context is continuously monitored. If the defined security policies are no longer met, access is immediately denied. Even if a user account or device is compromised, access remains limited to the applications that have been explicitly approved. As a result, ZTNA significantly reduces the attack surface.
ZTNA is a core feature of beem and works together with other beem components, including passkeys, beem Device Management, Identity and Access Management, the Business Application Portal, and the beem app. Together, these components form a comprehensive and user-friendly security architecture.
Context-based access
In addition to user identity, ZTNA uses contextual information to evaluate access requests. This allows organisations to precisely define who may access which application and under which conditions access is permitted.
Typical criteria include:
- User or user group
- Device used
- Device status (e.g., managed device)
- Location or network
- Date and time
- Access method (e.g., beem app)
These criteria can define access contexts such as the following:
A sales employee is granted access to the CRM system only if they have successfully authenticated, are using a managed corporate device, and are accessing the system from Switzerland.
ZTNA policies can be configured in Concerto.
INFO
ZTNA is available in the Standard, Plus, and Premium editions.
Firewall as a Service
Firewall as a Service (FWaaS) offers the ability to identify applications through various characteristics, such as Layer 7 Deep Packet Inspection (DPI), URL, protocol and port numbers, destination IP addresses, and more. This is used in combination with comprehensive, rule-based control. The DNS proxy secures DNS entries through information from authoritative DNS servers and DNS reputation feeds to block access to untrusted or malicious websites. URL and IP reputation, categorisation, and filtering enable safe browsing and block harmful websites. The TLS/SSL proxy opens and inspects encrypted traffic to detect threats and prevent data leaks. IPS detects and prevents the exploitation of vulnerabilities based on signatures and anomalies. Vulnerability signatures and anomaly detection are updated in real time to ensure continuous protection.
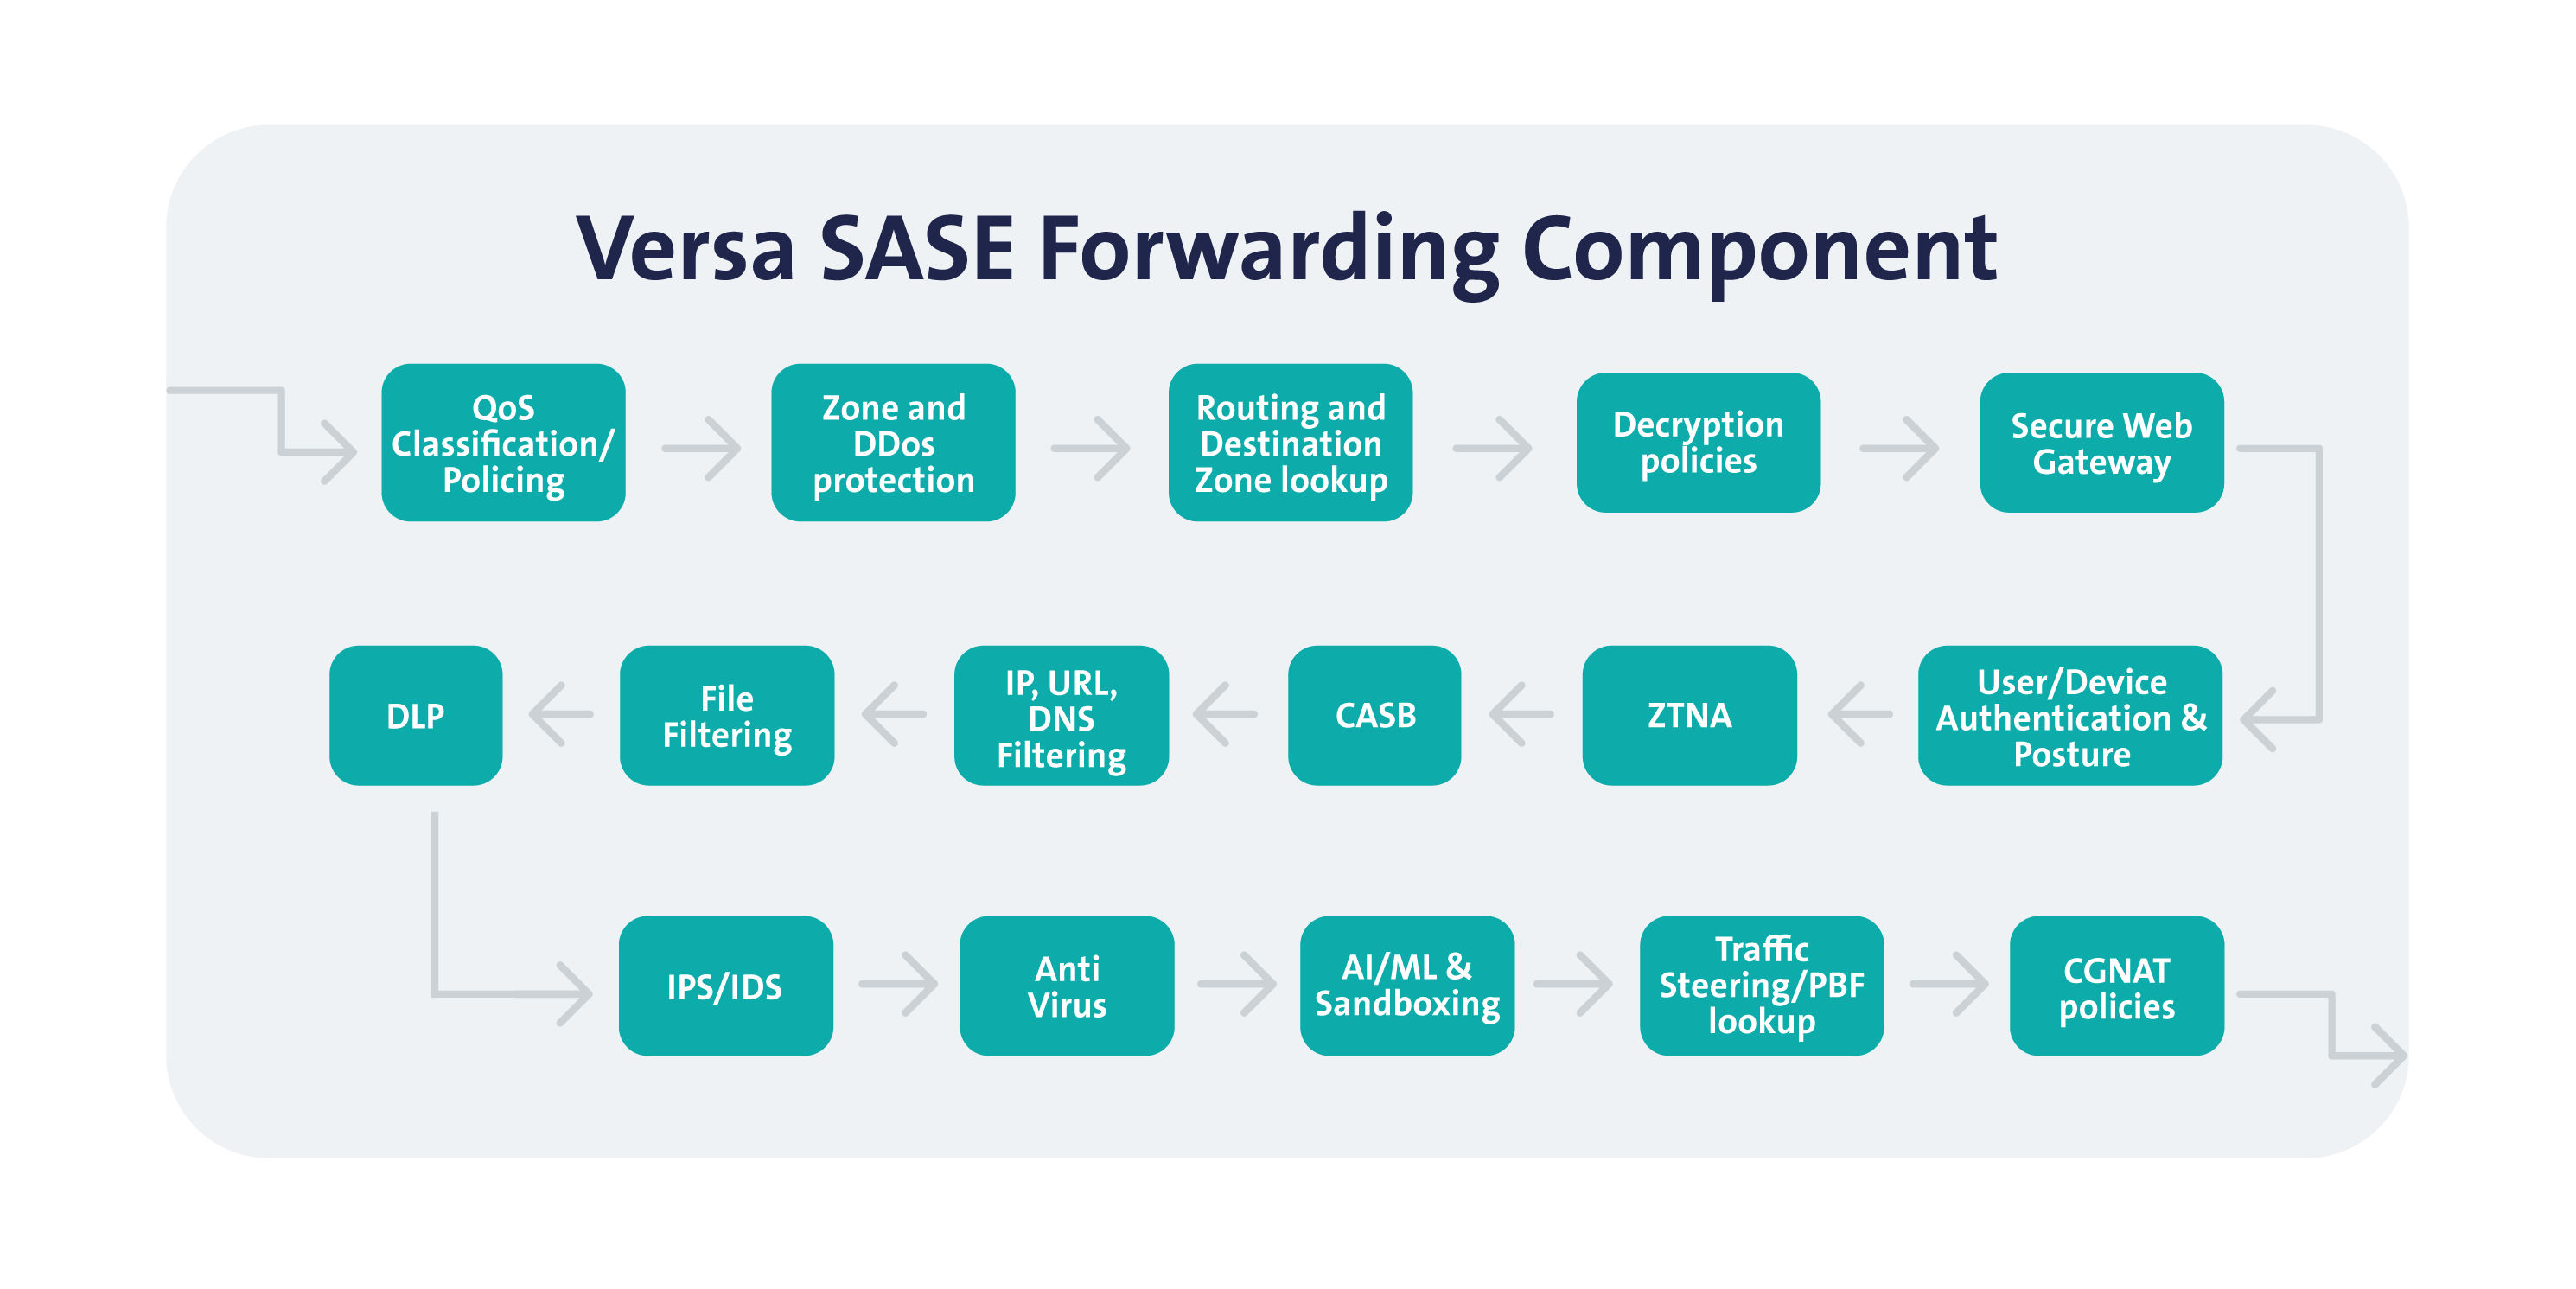 Figure: Versa SASE Forwarding Component illustrating the layered security and traffic processing pipeline within beemNet’s infrastructure.
Efficient management, protection, and monitoring form the foundations of secure web access control. Predefined policies and bandwidth prioritisation optimise web traffic. Threat defence provides comprehensive protection against malicious websites and enables a quick response to new attack patterns. Real-time data leak prevention blocks unauthorised data transmissions and ensures compliance with regulations. Security for mobile employees enables protected web access from any site and device. Real-time monitoring ensures seamless control and blocking of inappropriate content to guarantee secure and managed web access. Together, these components form a holistic security solution for secure and managed web access:
- Stateful Firewall
- Application Visibility
- Next-Generation Firewall
- IP-Filtering
Stateful Packet Inspection
Stateful Packet Inspection (SPI) is a core security capability integrated into beem's SASE platform to provide intelligent, context-aware firewall protection for all internet-bound traffic. Unlike stateless filtering, which only evaluates individual packets, SPI tracks the entire state and context of network sessions, enabling the platform to make informed decisions about traffic legitimacy. In beem, SPI is enforced through Internet Protection Rules, which are applied per beem tenant and dynamically evaluate traffic based on a combination of match criteria (e.g., applications, users, geolocation, IP addresses, and protocols) and predefined security enforcement actions (e.g., allow, deny, or profile-based inspection). SPI ensures that traffic is evaluated not only by source and destination but also based on behavioural patterns and protocol compliance. For example, it can recognise and validate the proper sequence of a TCP handshake or detect deviations from normal session behaviour, rejecting suspicious or malformed connections automatically. The inspection logic is embedded into the firewall enforcement engine and works in concert with:
- Application and URL filtering
- IPS (Intrusion Prevention System)
- Deep Packet Inspection (DPI)
- TLS/SSL decryption
- IP reputation and DNS security
- Role- and identity-based access policies
This layered approach allows SPI to be highly effective at detecting session hijacking, protocol abuse, and spoofed connections while maintaining performance through optimised processing at the point of presence (PoP). As part of the beemNet architecture, SPI plays a key role in delivering secure and policy-compliant internet access for both fixed and mobile users, aligned with Swisscom's security tiers.
Deep Packet Inspection
Deep Packet Inspection (DPI) is a key inspection technique used in beem's SASE-based beemNet infrastructure. It analyses the full payload of data packets, not just header information, to detect and control complex traffic patterns and threats in real time. DPI enables advanced visibility and filtering by examining the content of internet traffic, allowing for enforcement based on:
- Protocol compliance and anomalies
- Application signatures and behaviours
- Embedded malware, spyware, or other threats
- Potential data leaks (DLP)
- Policy violations and inappropriate content
In beem, DPI is primarily activated from Security Level 2 upwards. At this level, traffic, including encrypted connections, is decrypted by the TLS/SSL proxy and inspected inline. DPI works in conjunction with:
- Stateful Packet Inspection (SPI)
- URL and IP filtering
- Antivirus and anti-malware engines
- Intrusion Detection and Prevention Systems (IDS/IPS)
DPI is essential for detecting advanced threats that bypass traditional firewalls and enables the application of granular security controls. Its effectiveness relies on continuous updates to protocol recognition, threat signatures, and behavioural heuristics. As part of the beemNet security stack, DPI contributes significantly to the ability to block malicious content, enforce usage policies, and ensure regulatory compliance—all while maintaining a seamless user experience.
DNS proxy and security
DNS Proxy and Security is a comprehensive solution designed to protect networks and clients at the DNS layer by combining advanced filtering, threat intelligence, and traffic management capabilities. It includes the following core components: DNS Forwarder, DNS Split Proxy, DNS Proxy, DNS Threat Feeds, and DNS Firewall.
- The DNS Proxy plays a central role in securing DNS traffic. It leverages information from authoritative DNS servers and continuously updated DNS Reputation Feeds to block access to untrusted, unknown, or malicious domains, including those associated with Command & Control (C&C) infrastructures used by attackers. It also improves DNS resolution speed and simplifies DNS management.
- DNS Security and Filtering protects against a wide range of DNS-based threats, including DNS hijacking, reflection and amplification attacks, spoofing, phishing, malware, ransomware, and botnets. This protection is enforced directly at the DNS layer, preventing threats before they reach the network or endpoints.
- The DNS Forwarder is used when a DNS server cannot resolve a query using its local DNS tables and must forward the request to an external resolver.
- The DNS Split Proxy enhances efficiency by separating internal (e.g., within a corporate domain) and external DNS queries, ensuring optimal routing and resolution performance.
- DNS Threat Feeds are dynamic, global datasets that provide real-time intelligence on malicious domains. These feeds are continuously updated using data from hundreds of sensors worldwide, enabling proactive blocking of newly registered or suspicious domains until their reputation is verified.
- The DNS Firewall inspects every DNS query and blocks access to domains identified as dangerous, such as phishing sites or compromised web servers, thereby adding another layer of security.
Together, these components form a robust DNS security architecture that not only accelerates domain resolution but also significantly reduces the attack surface by preventing access to harmful domains at the earliest possible stage.
URL and IP reputation
beem NGFW provides a rich set of URL and IP categorisation and filtering capabilities in 80+ URL categories to enable safe browsing while blocking malicious sites. The URLs are categorised by reputation, risk, and trustworthiness. In addition to predefined classes, beem provides support for user-defined/custom classes that can be created and managed as needed. Hundreds of millions of domains and 13+ billion URLs are scored and classified for maximum threat coverage.
The predefined categories cover generative AI and general internet sites to improve employee productivity, inappropriate sites such as gambling or pornography to avoid legal liability, and voice and video sites for bandwidth management.
- Periodic URL database updates via security packages, without VOS or software upgrades
- Real-time cloud lookups for URLs not categorised in the VOS cache
- Custom URL categories based on regex and/or fixed string match
- Customisable captive portal screens for policy enforcement and redirection
- Support for Block, Inform, Ask, Justify, Override, and Authenticate pages
TLS and SSL proxy and decryption
- Protects against threats hidden in encrypted traffic by breaking open and inspecting TLS/SSL traffic and applying additional security policies for threat and data protection.
- Directs encrypted traffic based on application signatures, scans encrypted content for malware and exploit prevention, and detects and prevents data leakage to enforce company compliance.
- Supports transparent or split-proxy modes.
- Supports TLS versions 1.0, 1.1, 1.2, and 1.3 and has been ahead of many security vendors in support for TLS 1.3. beem recommends using TLS 1.3 with the TLS proxy for higher security, as it improves the confidentiality and integrity of communications.
- Perfect Forward Secrecy (PFS) uses ephemeral keys to overcome confidentiality concerns. PFS is mandatory with TLS 1.3. By generating a unique session key for every session that a user initiates, even the compromise of a single session key will not affect any data other than that exchanged in the specific session protected by that particular key.
- Parts of the handshake (server certificate values such as CName and SAN) are encrypted. This prevents malicious third parties (who rely on examining server certificates) from eavesdropping on the connection.
Intrusion Detection System
An Intrusion Detection System (IDS) is a passive monitoring component used to analyse network traffic and identify suspicious or unauthorised activity. It operates out-of-band, meaning it receives a mirrored copy of the traffic rather than being inline with the flow. The IDS inspects the traffic using:
- Signature-based detection: Compares traffic patterns against a regularly updated database of known threat signatures.
- Anomaly-based detection: Identifies deviations from established traffic baselines to detect novel or zero-day attacks.
Administrators can define vulnerability profiles that specify detection rules, thresholds, and response actions (e.g., alerting or logging). These profiles can be:
- Predefined, covering typical use cases like client protection, malware detection, or OS-specific threats.
- Customised, where rules are adapted to organisational needs (e.g., filtered by CVSS score, operating system, or traffic direction).
The IDS logs detected events and optionally captures packet data for further analysis. These logs and captures are typically forwarded to a centralised analytics system for visibility and correlation. By placing IDS at internal junctions (e.g., between VLANs or critical systems), organisations gain deep visibility into east-west traffic, helping to detect lateral movement or insider threats.
Intrusion Prevention System
An Intrusion Prevention System (IPS) is an inline security mechanism that not only detects malicious activity but actively blocks it. Unlike IDS, the IPS sits directly in the traffic path and can drop or reject packets in real time. All traffic passes through the IPS before being forwarded, allowing immediate response to detected threats. Detection methods include:
- Signature-based detection: Matches incoming traffic against a curated database of known attack signatures.
- Anomaly-based detection: Compares real-time traffic behaviour against established baselines to detect unusual activity.
Actions that can be enforced by the IPS include:
- Dropping malicious packets or entire sessions
- Resetting connections from client or server side
- Logging events with optional packet capture
- Generating alerts for security teams
The system uses vulnerability profiles—collections of detection rules categorised by criteria such as:
- CVSS score range
- Operating system or application
- Attack vector or protocol
- Rule type (signature or anomaly)
Profiles can be predefined or custom-built using a rule editor that allows filtering by threat ID, severity, or detection confidence. Additionally, administrators can upload their own custom rules in standard formats (e.g., Snort-compatible), which are compiled and applied to traffic. To avoid service disruption, the system supports asynchronous rule compilation, meaning new rules can be prepared in the background while previous ones remain active. For fine-grained control, thresholds and exceptions can be configured—allowing, for instance, specific IP addresses to bypass certain rules, or limiting actions based on hit rates within defined time intervals. An IPS plays a critical role in preventing exploitation of vulnerabilities and ensuring that unauthorised traffic is intercepted before it reaches protected resources.
Malware and antivirus scanning
Malware protection is a core element of the beemNet security stack and is designed to detect and block malicious software before it can compromise endpoints or networks. This includes threats such as viruses, worms, Trojans, ransomware, spyware, and other unwanted code that may attempt to exfiltrate data or disrupt services.
To ensure robust protection, beemNet integrates malware and antivirus (AV) scanning directly into its traffic inspection pipeline. This inspection is performed in real time and applies to both web and mail protocols, supporting:
- Multi-protocol inspection: Scans traffic over commonly used protocols including HTTP, HTTPS, FTP, SMTP, POP3, IMAP, and MAPI.
- Bidirectional analysis: Inspects both upload and download streams to identify malware attempting to enter or leave the network.
- File-type filtering: Filters based on file format, MIME type, or signature to prevent delivery of malicious content.
- Policy-based enforcement: Applies predefined or custom actions (e.g.,
Alert,Deny,Reject) in line with corporate security policies.
Beyond inline traffic, files can also be scanned offline in cloud storage or via API-driven inspection.
Threats are detected through:
- Signature-based detection: Matching files and payloads against a database of known malware hashes and patterns.
- Heuristics and behavioural analysis: Identifying suspicious behaviours, such as self-replication, code injection, or abnormal file system access.
- Real-time updates: Continuously updated signature databases to address newly discovered threats.
This capability is available from Security Level 2 onwards and plays a key role in protecting users across all connected networks.
Administrators can configure custom malware protection profiles, defining:
- The protocols and directions to scan (e.g., download only or both directions)
- File types or categories to include in the scanning scope
- Enforcement actions for detected threats:
Allow(log only)Alert(raise notification)Deny(block delivery)Reject(actively drop connection)Recommended Action(based on risk score or policy presets)
Profiles can also include tagging and metadata for filtering, reporting, and policy assignment. Logs from malware detection can be forwarded to a centralised analytics platform for correlation and incident response.
Combined with sandboxing, reputation services, and anomaly detection, malware and antivirus scanning forms a vital layer of a defence-in-depth strategy. It prevents compromise, data leakage, and system disruption across all connected devices and services, with minimal impact on performance.
Application Layer Gateway
The Application Layer Gateway (ALG) is a network function that facilitates the correct handling of application protocols requiring dynamic port assignments and embedded IP addressing, especially when traffic is subject to NAT (Network Address Translation) or firewall inspection. Certain protocols, such as FTP, SIP, PPTP, TFTP, and IKE ESP, establish secondary data sessions or include IP and port information in their payload. Without ALG, these sessions often fail when traversing NAT devices or strict firewalls, as dynamic connections are not correctly translated or allowed.
ALG operates by:
- Interpreting control traffic of specific application protocols
- Modifying embedded IP addresses and ports as needed for NAT traversal
- Dynamically creating temporary firewall rules (pinholes) to permit legitimate return traffic
- Maintaining session awareness to remove rules when sessions terminate
Example use case: FTP in active mode
In active FTP mode, two sessions are created:
- A control session (e.g., port 21) to manage commands like directory listing or file actions
- A data session where the server initiates a connection back to the client to transfer files
Without ALG, firewalls or NAT devices cannot recognise or permit the incoming data session, especially if the client resides behind a private IP address. ALG inspects the control channel, extracts the necessary IP/port information, rewrites it appropriately, and opens a pinhole in the firewall or NAT device to allow the session to succeed.
Data traffic optimisation
Although beem employs advanced security features, it still ensures a smooth and responsive user experience. This is achieved through intelligent traffic screening: beem distinguishes between data that requires inspection and data that is already verified as secure. Trusted traffic is routed directly to its destination instead of being re-inspected, preventing unnecessary use of system resources. Eliminating such redundancies optimises beemNet’s bandwidth utilisation, thereby delivering the best possible user experience.
The optimisation process covers all Swisscom-owned services (e.g., Voice over IP or content streaming via blue TV) as well as secure traffic from trusted third parties (e.g., communication or entertainment platforms). All optimisation is based on a Swisscom-managed whitelist consisting of static IP addresses classified as secure and non-shared.
Customised optimisation
Data traffic optimisation is actively managed by Swisscom. Upon request, Swisscom can define custom optimisation rules for individual companies and organisations. This feature is available exclusively for devices connected to beemNet via the beem app (agent-based). All other devices (agentless) follow the general optimisation rule set.
INFO
Optimised traffic does not appear as logged data in Concerto (SASE Web Monitoring).
Access network integration
Integration with beem Office via the beemNet option
The integration of beem Office with beemNet is achieved through a site-specific beemNet option. This enables all devices at that office site to be protected by the beemNet security perimeter. The beem Office router (e.g., Centro Business Router) establishes the connection to the beemNet PoPs, enabling secure, policy-enforced internet access for all connected devices.
Integration with Smart Business Connect (without BNS)
Smart Business Connect lines can be integrated into beemNet by activating a beemNet option for the respective connection. The integration currently supports only Smart Business Connect lines without the Business Network Solution (BNS) option. This limitation applies to the initial rollout phase of the beemNet integration.
Integration with NATEL® go via the beemNet option
Mobile users with a NATEL® go subscription can be integrated into the beemNet ecosystem through the activation of a user licence. Once linked to a user identity, traffic is secured through the beem app, ensuring encrypted, policy-compliant communication across any network (e.g., Wi-Fi, mobile).
Integration with Swisscom mobile network via Protect & Connect user licences
Users without a business mobile subscription can be onboarded with a Protect & Connect licence. This grants them access to the beemNet services on one device and includes the use of the beem app. The Protect & Connect licence ensures traffic is routed through the Swisscom security layer, applying all security levels and inspections.
Endpoint IP address cloaking
You can use the endpoint IP address cloaking feature for your beem-protected wireline connections to hide the public IP addresses of your client devices and sites. With cloaking enabled, your IP addresses are not visible outside your local network or on the internet. External entities such as website owners see only a generic public IP address. This reduces traceability and attack surface, and gives better protection against targeted attacks such as Denial-of-Service (DoS).
Endpoint IP address cloaking uses the Carrier-Grade Network Address Translation (CGNAT) technique. When IP cloaking is active, your traffic reaches the internet through a beem-owned pool of shared public IP addresses (geolocated in Switzerland) instead of your own public IP address.
Cloaking by Security Edition
- Essential Edition (always on): IP cloaking cannot be disabled. Public IPs and fixed WAN IPs are not available; port forwarding is not possible.
- Standard, Plus, and Premium Editions (optional): You can disable IP cloaking to use public IPs, including fixed WAN IP addresses.
Port forwarding
When endpoint IP address cloaking is active, port forwarding is not possible because no public IP address is provided. To enable port forwarding, you must first disable endpoint IP address cloaking and then set up the port forwarding rules.
1. Disable endpoint IP address cloaking in My Swisscom Business.
Inventory → Company → Location → select location → Internet → IP address cloaking or Hide IP Address (depending on your wireline product) → set toggle to Public.
2. Set up secure port forwarding with the Edge Interceptor configuration guide.
INFO
Endpoint IP address cloaking works only with IPv4, because CGNAT does not support IPv6.
Unified Threat Management
E-mail security for SMTP, IMAP, MAPI, and POP3
E-mail security is delivered via a proxy that inspects mail protocols such as SMTP, IMAP, POP3, and MAPI. The inspection includes:
- Signature-based malware detection
- Spam and phishing filtering
- Content and attachment scanning
- Blocking of malicious senders and domains
Fixed IPs are required for server-to-server communication. This feature is available starting with the Premium Security Edition and complements broader Data Loss Prevention (DLP) strategies.
Outbound traffic
Internet access via beemNet
All outbound internet traffic is routed through the beemNet infrastructure, applying policy enforcement at the DNS, IP, and application level. Users benefit from URL filtering, Deep Packet Inspection (DPI), TLS/SSL decryption, and threat reputation services. Swisscom may apply bandwidth throttling per device or site to ensure consistent protection levels across its shared infrastructure.
WARNING
Services that require public-facing IPs (e.g., dynDNS) are not compatible with beemNet due to IP cloaking.
Inbound traffic (access to private applications and networks)
The Edge Interceptor
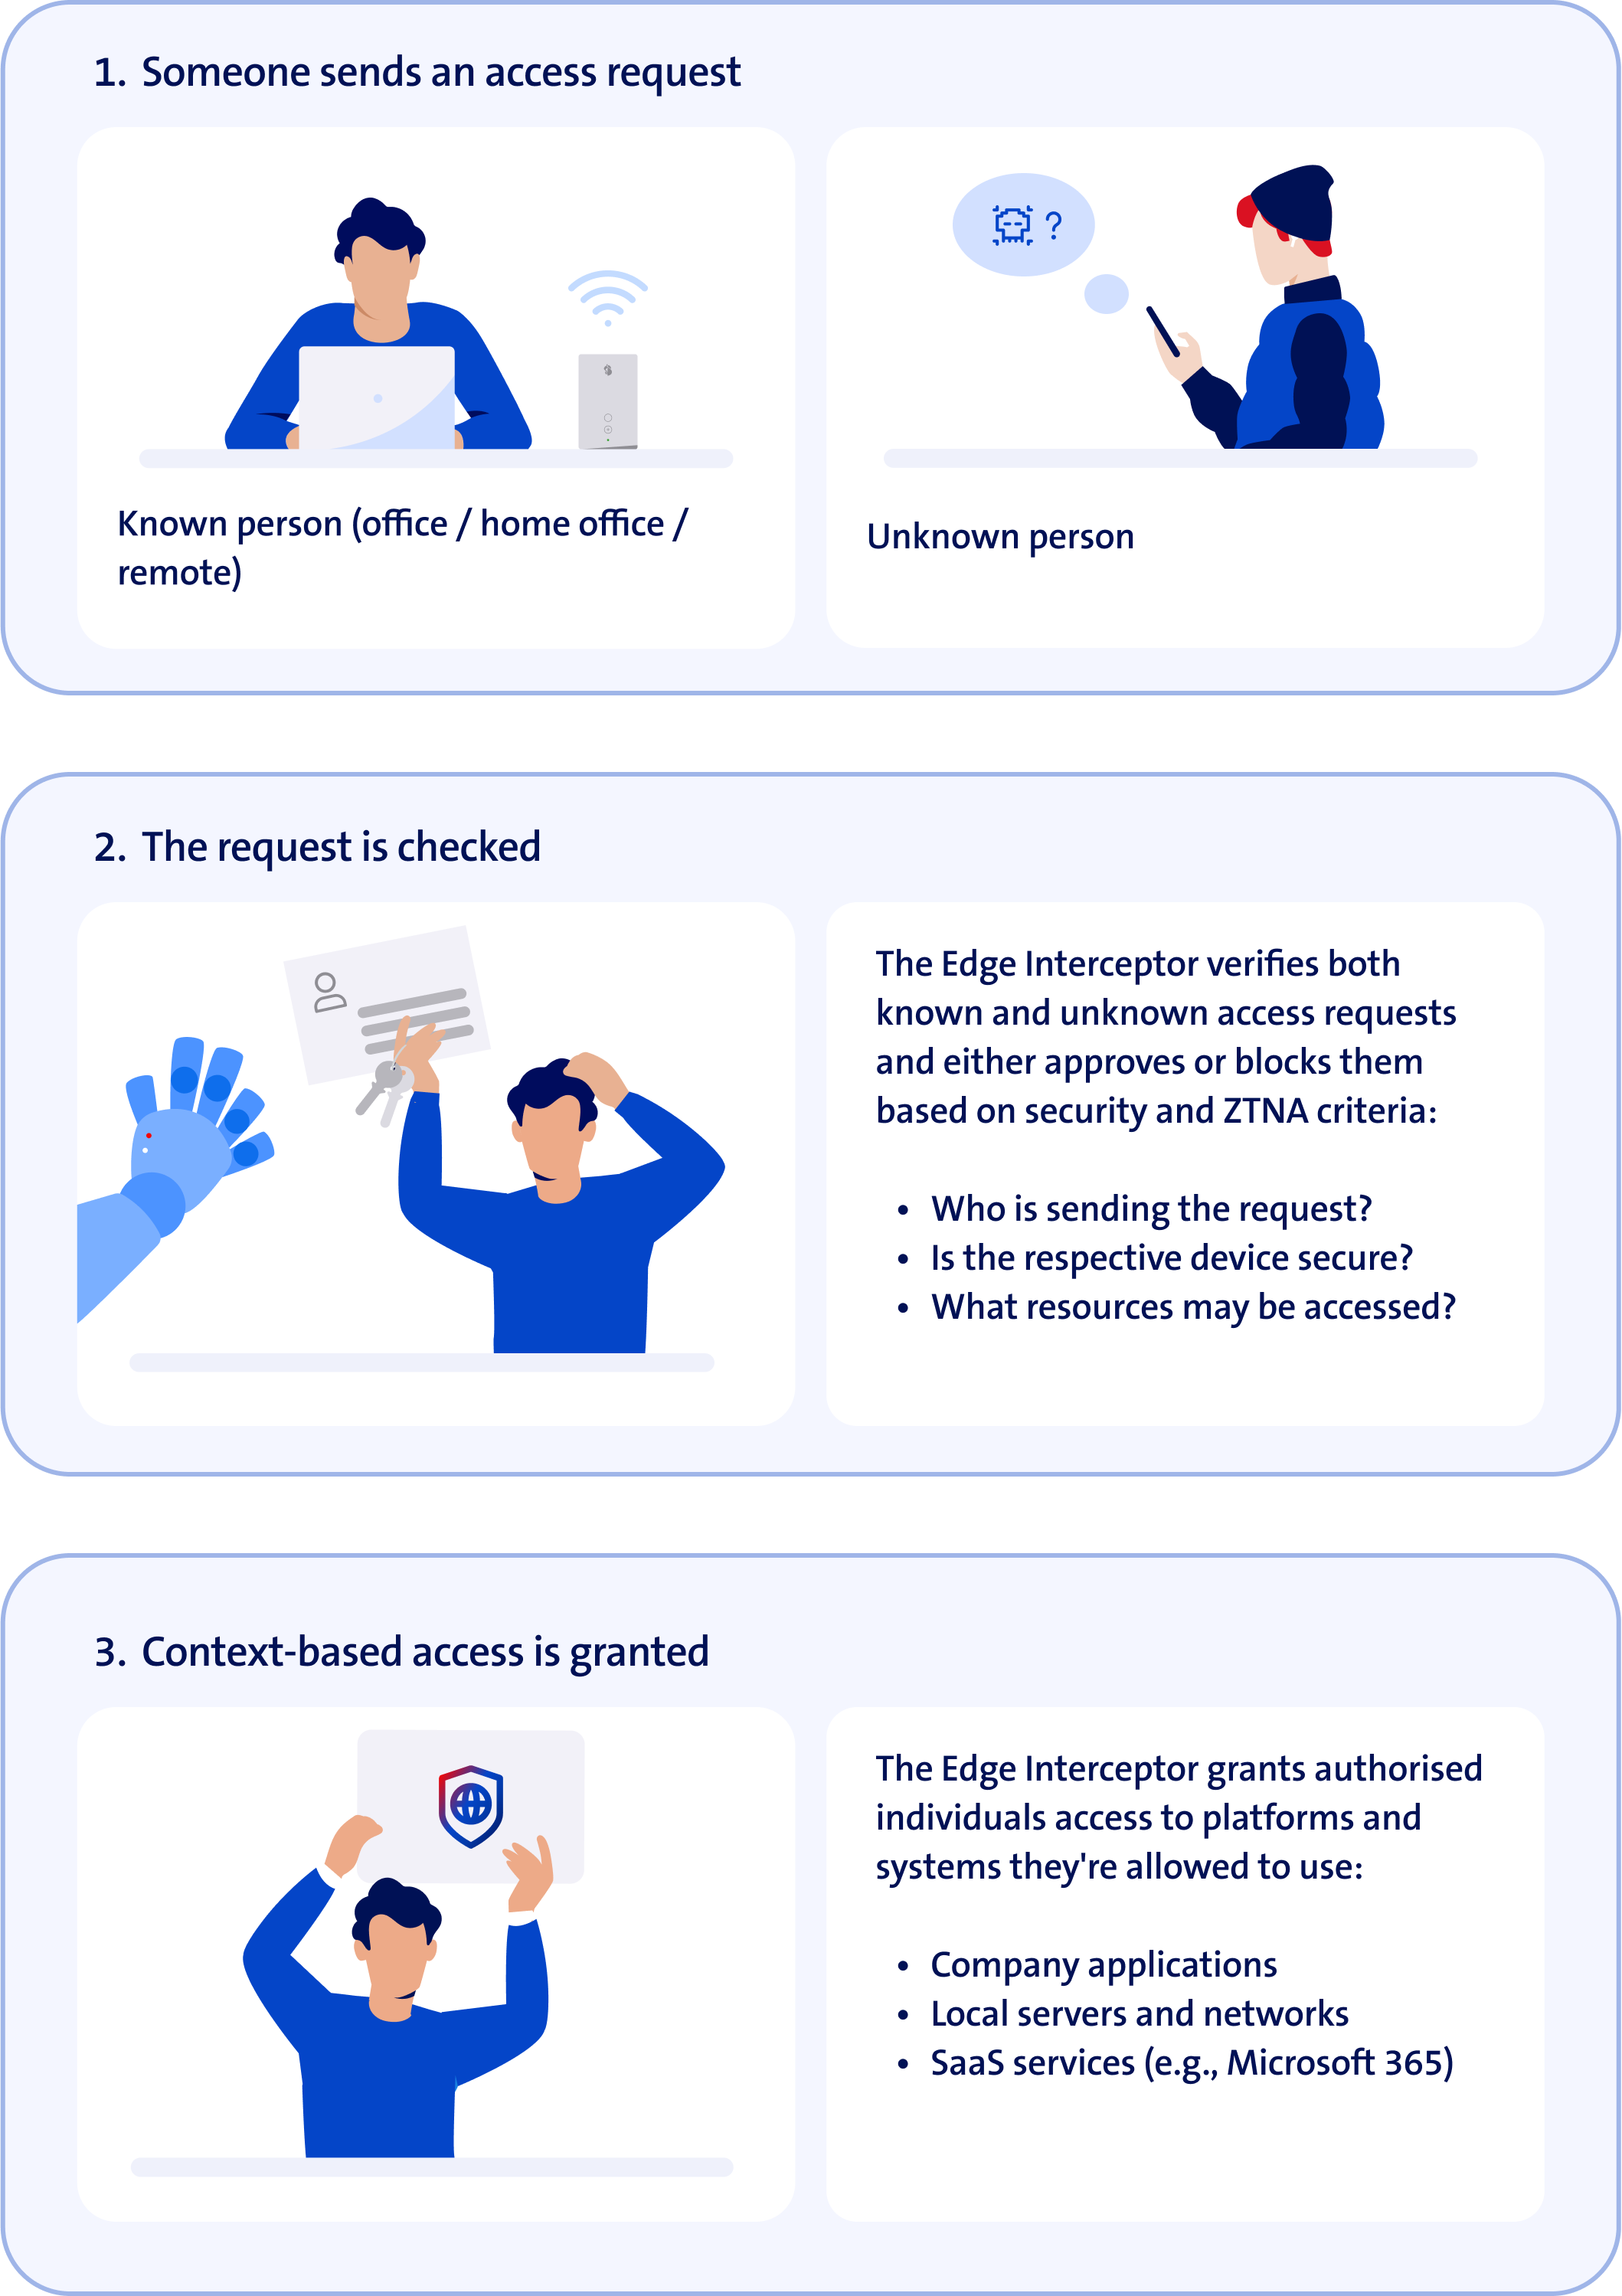
All inbound traffic to a beemNet-protected environment is denied by default, which keeps cyber threats out. However, this also means that legitimate access to beemNet-secured networks is blocked—for example, if an employee is working from home and needs access to a beemNet-protected company server.
To enable such access, beem offers the Edge Interceptor feature, which allows ZTNA-based secure access to company networks, servers, and applications. It intercepts incoming data traffic and, if allowed, securely routes it through beemNet to its correct destination.
Unlike conventional port forwarding, which poses an inherent security risk, the Edge Interceptor functions as a secure access point, enforcing beemNet security and ZTNA policies whilst not affecting existing firewall settings.
The following guides provide step-by-step instructions for configuring secure access to your beemNet-protected servers and private applications. Find your product-specific guide below and follow the corresponding configuration procedure.
On- and Off-Net distinction
When configuring the Edge Interceptor, it is important to distinguish between On-Net and Off-Net connections, as each has different implications for the setup process. The terms On- and Off-Net refer to where data traffic takes place: On-Net traffic stays within beemNet, while Off-Net traffic goes beyond it.
On-Net
On-Net means a user, device, or application connects from inside beemNet using Swisscom products like beem Office, Smart Business Connect, or Protect & Connect. In this case, the data traffic stays completely within Swisscom’s secure backbone and never goes out to the public internet. It is considered an internal, secure zone because all users and devices are verified through their beemNet product identity.
On-Net examples:
- An engineer works at one Smart Business Connect company site and accesses a server at the other protected company site.
- An employee on the road accesses a company application using his laptop whilst being online with a Protect & Connect Mobile SIM.
- Two company branches, both with beem Office, send files to each other.
Off-Net
Off-Net access, on the other hand, is initiated from outside the beemNet ecosystem over the public internet. In this case, the Edge Interceptor acts like a protective gateway, applying ZTNA-based access rules before allowing entry. Although Off-Net traffic travels a riskier path through the public internet, the Edge Interceptor enables secure and controlled inbound traffic and external access.
Off-Net examples:
- An employee works remotely on hotel Wi-Fi and uses the beem app to access a company application.
- A business partner needs to establish a connection to a beemNet-protected company NAS from their own internet provider.
- A company's cloud server on AWS receives traffic from online customers, whose requests are filtered and forwarded safely into beemNet.
INFO
For beem Office and Smart Business Connect, access to private applications is available with the Standard, Plus, and Premium beem Security Editions.
For Enterprise Connect, access to private applications is available with the Plus and Premium beem Security Editions.
Additional products and configuration options will be introduced as beemNet capabilities expand.
Inbound traffic configuration guides
beem Office, Smart Business Connect and Enterprise Connect XS
On-Net configuration guide
This guide explains how to configure secure On-Net access using a Centro Business Router and integrate it with Concerto’s security and ZTNA policies. Because On-Net connections operate entirely within beemNet, no VPNs or tunnels are required. Your beemNet-protected systems can be accessed through securely exposed IP addresses.
Both solicited and unsolicited inbound connections can be set up using the same procedure (part 2), but each must be configured separately.
- Open the Centro Business Router Admin Dashboard.
Navigate toNetwork→Port Forwarding. - Click on
Add new rule. - Select a public IP.
- Choose a port.
- Choose the LAN IP of the target system.
- For
Local Port, chooseSame PortorCustom Defined. - Save the configuration.
Open Concerto and navigate to
Configure→Real-Time Protection→Private App Protectionand click on Add + to start the set-up process.Step 1
Applications: Skip this step.Step 2
User & Groups:- To enable solicited inbound traffic, select User groups. In the customisation options, select
managed-profile-saml-oneidband choose the user group you want to enable inbound traffic for. - To enable unsolicited inbound traffic, select User device groups and select the option
VSIA_VSPA-Default.
- To enable solicited inbound traffic, select User groups. In the customisation options, select
Step 3
Endpoint Posture: Skip this step.Step 4
GEO Locations: Skip this step.Step 5
Network Layer 3-4: Open theDestination Addresstab and click on Add Adress Group. Enter the fixed public IP address of your Centro Business Router (including the subnet, e.g., ".xx/32") and define a name and tag.Step 6
Security Enforcement: Select Allow.Step 7
Review and Deploy: Check and save your configurations.
Once you have completed the set-up process and are back on the Private App Protection page, make sure to click on Publish to finish the set-up.
Off-Net configuration
Off-Net access is established by setting up site-to-site VPN tunnels for all beemNet gateways. The beemNet infrastructure consists of four geographically redundant Points of Presence (PoPs) in Switzerland, each equipped with an automatic failover mechanism. This results in a total of eight gateways—four active and four on standby—that must all be connected through secure tunnels to ensure optimal connectivity and redundancy.
This process is complex and currently cannot be carried out through a streamlined, user-friendly interface. Therefore, please contact Swisscom if you need to set up Off-Net connections. Once set up, you can manage your company's security and zero-trust policies in Concerto as usual.
Enterprise Connect Central Internet
This guide explains how to set up secure access using the Enterprise Connect Dashboard and Concerto. This is done by creating an outbound VPN link to establish a secure network path, configuring port forwarding to route incoming traffic from a public IP to the correct internal server, and applying Concerto’s security and ZTNA policies to permit inbound traffic and access.
Access for solicited and unsolicited traffic can be configured using the same process (part 3), but each must be set up separately.
- Open the Enterprise Connect Dashboard and navigate to
Network Services→Settings. - Look for the
beemtile and make sure the status isOn. - Navigate to
Securityand click on theOutbound Linkstile. - Click + to generate a VPN-specific outbound link. Accept this configuration by clicking on the checkmark and then save.
- Go to the checkout in the top-right corner and submit your configurations.
- Open the Enterprise Connect Dashboard and navigate to
Network Services→Security. - Click on the
S-SPAT-Linkstile and then on + to add a new rule:- Enter a name and your public IP.
- Choose Source VPN.
- Enter the private IP address of the destination server.
- Choose the protocol (TCP/UDP).
- Configure
Origin Destination Ports. - Configure
Translated Destination Ports.
- Confirm with the checkmark and go to the checkout in the top-right corner to submit your configurations.
Open Concerto and navigate to
Configure→Real-Time Protection→Private App Protectionand click on Add + to start the set-up process.Step 1
Applications: Skip this step.Step 2
User & Groups:- To enable solicited inbound traffic, select User groups. In the customisation options, select
managed-profile-saml-oneidband choose the user group you want to enable inbound traffic for. - To enable unsolicited inbound traffic, select User device groups and select the option
VSIA_VSPA-Default.
- To enable solicited inbound traffic, select User groups. In the customisation options, select
Step 3
Endpoint Posture: Skip this step.Step 4
GEO Locations: Skip this step.Step 5
Network Layer 3-4: Open theDestination Addresstab and click on Add Adress Group. Enter the IP address of the outbound VPN link configured in part 1.Step 6
Security Enforcement: Select Allow.Step 7
Review and Deploy: Check and save your configurations.
Once you have completed the set-up process and are back on the Private App Protection page, make sure to click on Publish to finish the set-up.